
See what is exposed
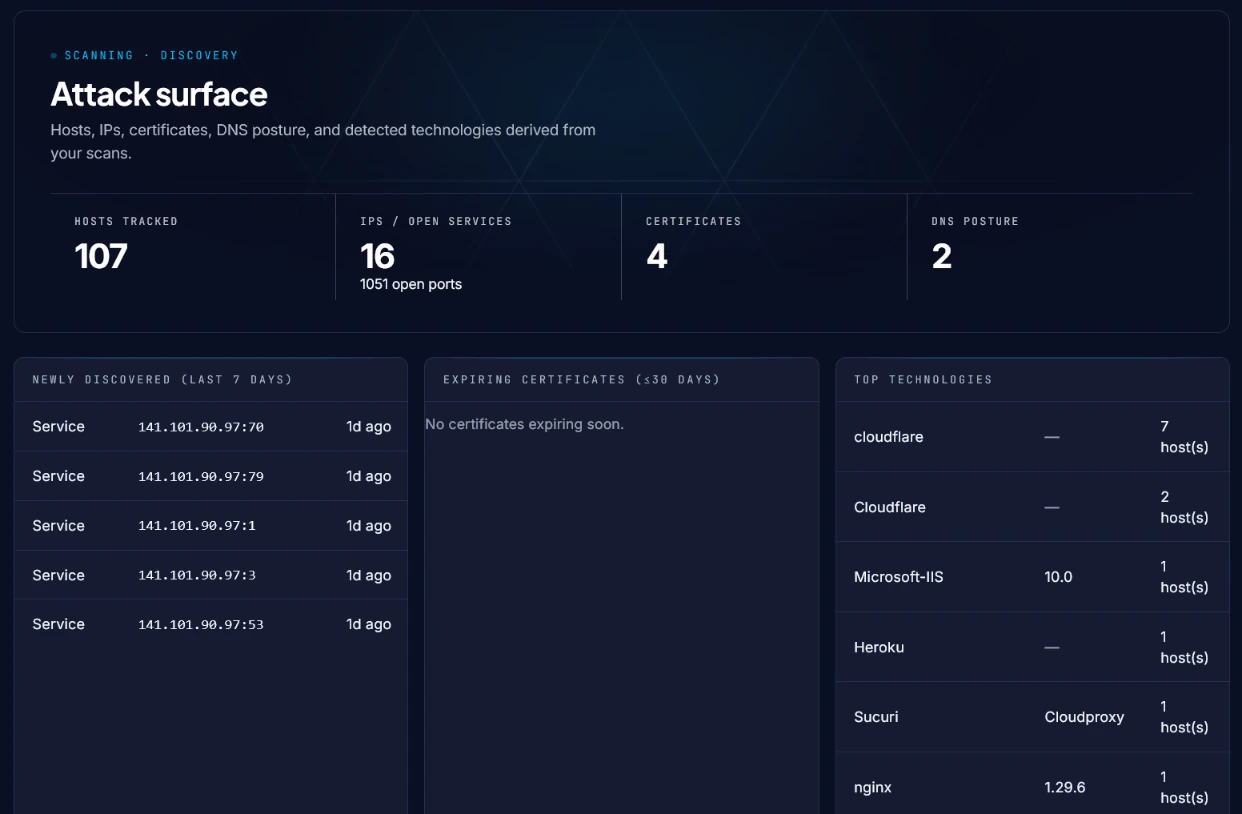
Track known assets and catch new external exposure as it appears, down to forgotten subdomains and services.
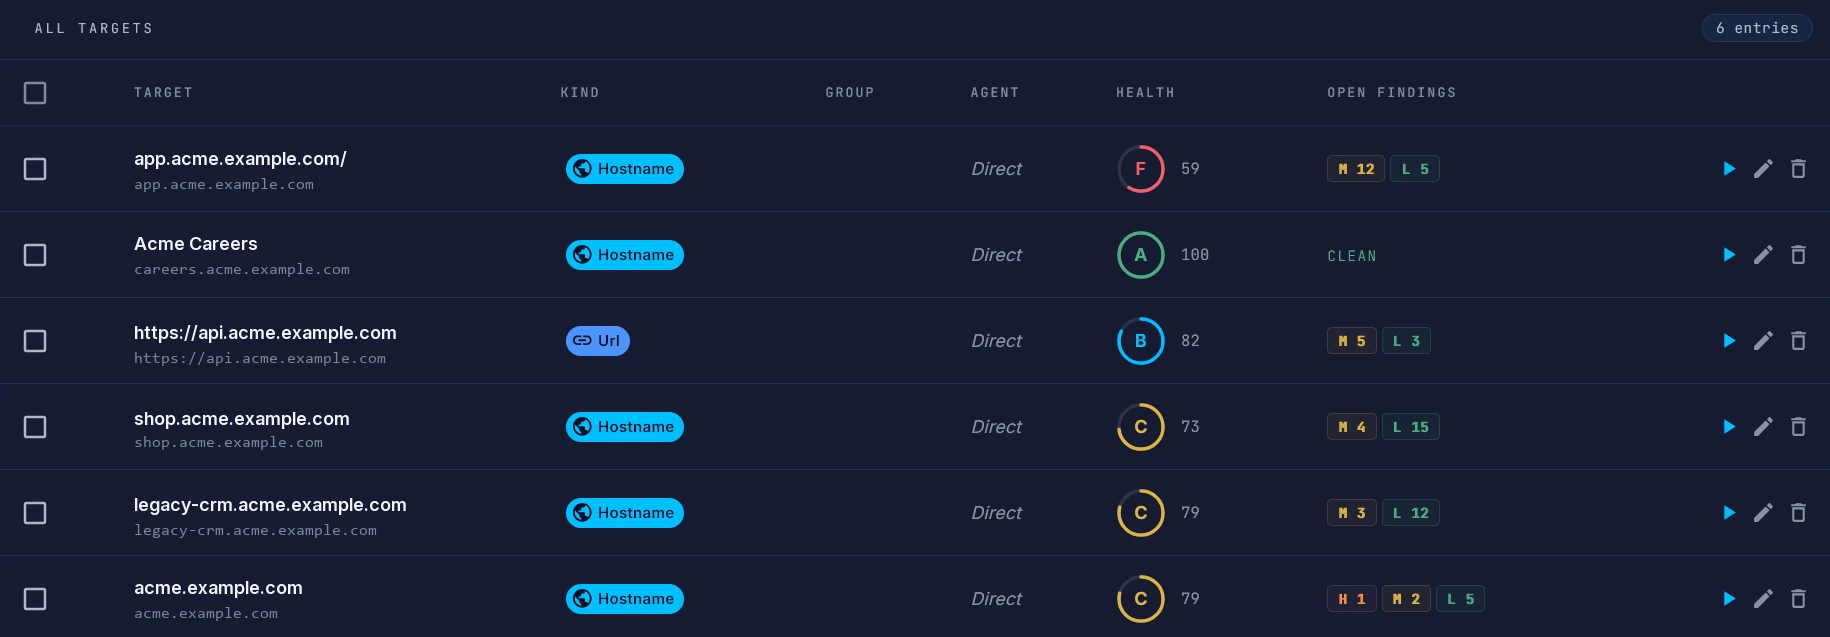

Attack surface, web app, network, code and cloud security in one platform. Continuous detection. Remediation guided by risk. Audit evidence built in. For teams tired of the noise.
Continuous monitoring Audit evidence 14-day trial EU-hosted
Preview of Vornin web app with representative scan data
Use Vornin to run the whole vulnerability management lifecycle on one record: find exposure, drive remediation to a verified fix, and keep the evidence attached.
One scan covers your attack surface, web apps, APIs, networks, code, containers and cloud. Every finding dedupes to one record.
Get real-world risk ranking (EPSS, KEV), AI-reviewed findings with fix guidance, SLA tracking and auto escalation for missed deadlines. Scans auto close findings when an issue no longer appears.
Each finding maps to the controls it touches and carries a tamper-evident history for your auditor.
Discover assets, assign owners, track SLAs, verify fixes and report from the same finding record.
Track known assets and catch new external exposure as it appears, down to forgotten subdomains and services.
Rank persistent findings by real-world risk, affected assets and exploitability, on one record that survives every rescan.

Daily sweeps flag new assets and alert you when known-exploited vulnerabilities (CISA KEV) match your confirmed stack.
Findings map to their controls as you work, so remediation becomes audit evidence, not a separate write-up.


Give engineers plain-language remediation guidance, create issues in Jira, GitHub, GitLab or Azure DevOps, and keep status tied to the original finding.
 Critical vulnerability
Generate executive, technical and compliance reports from the same data, with no spreadsheet rebuild.


Every finding enters the same queue, risk model and reporting workflow, regardless of where it was found.
See the public edge
Scan web applications, APIs and your external attack surface from the outside.
Inspect the systems beneath it
Scan network services, cloud posture across AWS, Azure and Google Cloud, containers and Kubernetes.
Catch risk before release
Scan code, secrets and dependencies before release. SAST detects 95% of OWASP Benchmark vulnerabilities.
Show auditors the recorded lifecycle, relevant control mappings, supporting evidence and chain-verification result.
Each finding maps to the framework controls it touches, automatically.
Every status change writes to a per-tenant, tamper-evident chain sealed with SHA-256. Change a record after the fact and the chain breaks.
Export any finding as an auditor pack: lifecycle, evidence and chain verification in one file.
sha256:8f3a...b912 VerifiedNIS2DORAISO 27001SOC 2PCI DSSHIPAAGDPRNIST 800-53CIS Controls
See all compliance mappingsVornin combines rule-based detection with AI false-positive review, EU data residency and persistent finding history, turning scan findings into evidence for the compliance controls they touch.
Defined scan checks produce every finding and rules set its priority, so the same input gives the same answer. AI reviews every code finding for false positives, writes context and fix guidance, and triages on request.
Vornin is a European company under EU jurisdiction, not the US CLOUD Act. Your scan data, findings, and audit evidence are stored and processed in the EU, AI included. Sub-processors.
One persistent record for each finding reduces noise and improves lifecycle tracking. Ownership, remediation, verification and evidence remain attached from detection to closure.
No demo required. Run a free scan and check transparent pricing before committing. Free includes web and network scanning, plus manual dependency and secret scans on one repository. Paid plans add advanced code and cloud scanning.
Understand scanning coverage, compliance scope, EU hosting, integrations and how signup works.
Vornin is a European vulnerability management platform. It scans your external attack surface, web apps, APIs, networks, code, containers and cloud, drives every finding to a confirmed fix, and turns that work into tamper-evident audit evidence.
Yes, Vornin includes scanning of multiple attack surfaces, from web apps, APIs and internal and external networks to code, containers and cloud, combining deterministic checks with context-aware AI to reduce noise. Each flaw keeps one record across scans and is ranked by real risk using layered threat intel. Each vulnerability is tracked through its lifecycle and closed automatically when a rescan confirms the fix. Audit evidence is built in. Security work is mapped to the technical controls it touches across nine frameworks, in a tamper-evident audit trail.
Yes, AI is used to enhance detection and reduce noise. Defined scan checks find every issue. AI then reviews every code finding for false positives, writes plain-language context and fix guidance for every finding, and triages exploitability on request. AI cannot hallucinate findings. Priority stays rule-based, using the world's leading threat intelligence such as the Exploit Prediction Scoring System (EPSS) and the CISA KEV catalogue to measure real-world exploitability. All AI processing runs in the EU.
Your external attack surface, web apps and APIs, internal and external networks, source code with its secrets, dependencies and infrastructure-as-code, container images and Kubernetes, and cloud posture across AWS, Azure and Google Cloud. One platform, one findings list across every scan type.
No tool can. Vornin maps findings to the technological controls it can test and gives you tamper-evident evidence of the work. Read the NIS2 compliance guide or the DORA compliance guide for what each framework actually requires. It reports control health honestly and never fakes a score for controls a scanner cannot check. Certifying your organisation stays your auditor's job.
Vornin is a European company, a Danish ApS, with no US parent, and is not subject to the US CLOUD Act. Your vulnerability data, findings and audit evidence are stored in the EU under EU law, AI processing included.
No. Code scanning uses read-only access. Vornin reads what it needs to scan and removes the working checkout. Selected redacted source excerpts remain as finding evidence under your plan's retention policy. Scanning does not write to your repository.
Yes. Vornin's integrations import findings from other scanners, create issues in GitHub, GitLab, Azure DevOps and Jira, add PR comments in GitHub, GitLab and Azure DevOps, and export to CSV, SARIF and SBOM. Vornin does not need to replace your stack to run the lifecycle on top of it.
No. Add your first target and scan in minutes. Free, Team and Business are self-serve with published pricing. Only Scale adds a short setup conversation.
Add a target and see Vornin turn scan findings into evidence.
No credit card required Read-only access EU-hosted
